
India
From Shy Voices to Confident Entrepreneurs: Bonda Women Step Beyond Their Villages

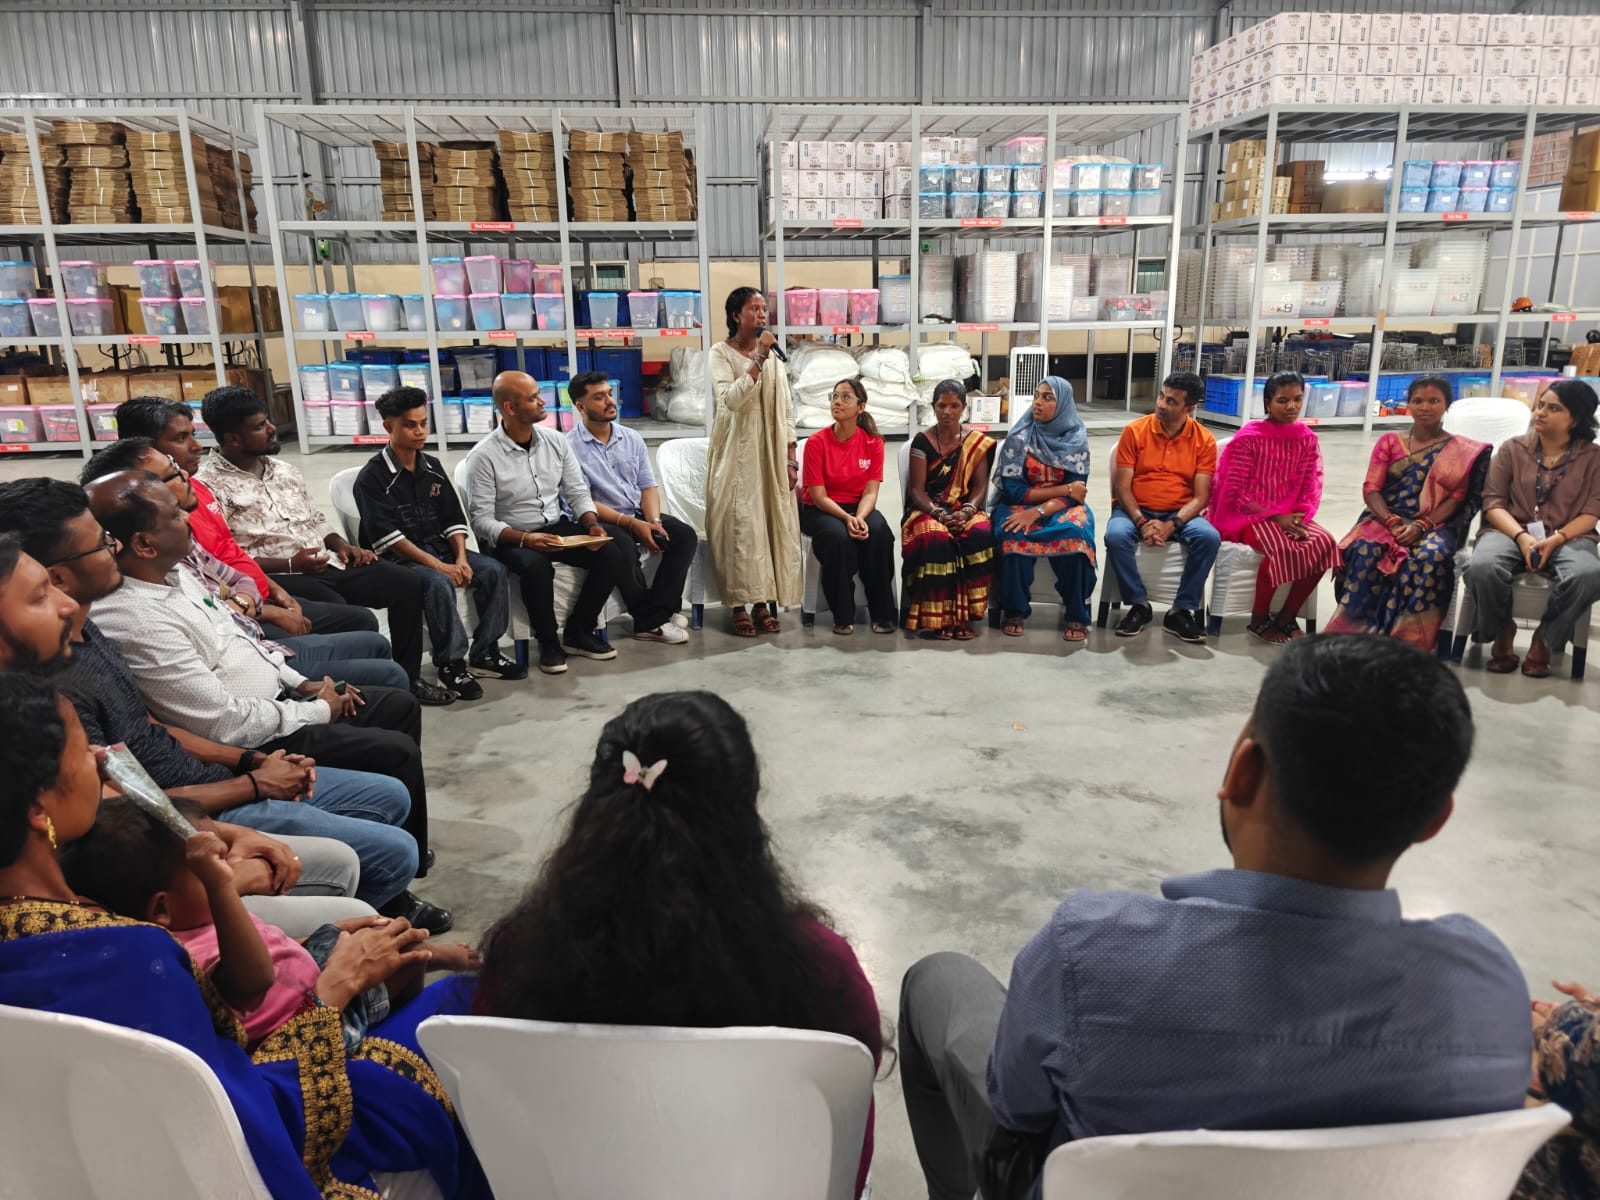
Bengaluru, August 15, 2026: Seven executive members of a Farmer Producer Company (FPC), all women from the Bonda tribe, one of India’s Particularly Vulnerable Tribal Groups (PVTGs), have travelled from the remote Bonda Hills of Odisha’s Malkangiri district to Bengaluru for a training programme on food drying and processing techniques at Jain University.
The training is part of a livelihood initiative implemented by Rise Against Hunger India to help increase household incomes through the processing and value addition of locally available forest produce, including bamboo shoots, jackfruit, mangoes and edible forest leaves.
The visit marks a significant milestone for the women, who are now directors and office bearers of their Farmer Producer Company (FPC). Three years ago, when Rise Against Hunger India began working with the community, many of them were hesitant to speak even in group settings. Today, they actively participate in discussions, ask questions and make decisions for their enterprise.
Their journey from shy participants to leaders of a collective enterprise reflects a deeper transformation rooted in confidence, agency and a growing belief in their own potential.
For many of the women, this is their first journey outside their region and their first experience of life in a major city. Beyond technical skills, the programme is providing exposure to new environments, people and opportunities while building on the community’s traditional knowledge of forest resources.
“The transformation we have witnessed among these women over the past three years is deeply encouraging. The fact that they are now travelling far from their villages, participating actively in a technical training programme and representing their producer company reflects how significantly their confidence and leadership have grown. Our aim is not to move communities away from their identity, but to help them build on their strengths and connect their traditional knowledge with opportunities that promote dignity and sustainable livelihoods,” said Dola Mohapatra, Chief Executive Officer, Rise Against Hunger India.
For the participants, the visit represents far more than a training opportunity.
“This is the first time I have travelled so far from my village. We used to see big buildings and cities only in movies. Travelling to Bengaluru, seeing tall buildings, riding the Metro, trying new food and meeting new people has been a completely new experience for me,” said Adibari Sisa, Executive Member, Amakund Farmer Producer Company.
“Being part of the producer company has given me confidence. Earlier, I only had dreams that I could do something meaningful. Now, I can see those dreams becoming a reality. This experience has shown me that women can be leaders and create positive change in their communities,” said Laxmi Badanayak, President of the Farmer Producer Company.
The NTFP training programme is part of Rise Against Hunger India’s broader efforts to strengthen community-led livelihoods and resilient local enterprises. By combining technical skill development, exposure and collective decision-making, the organization is supporting communities to create sustainable economic opportunities on their own terms.
About Rise Against Hunger India
Rise Against Hunger India is committed to ending hunger and improving lives through programmes focused on food security, nutrition, sustainable agriculture, women’s empowerment and livelihood development. The organisation works with vulnerable communities across India to build resilience, improve well-being and create pathways to sustainable development.
Over the past decade, Rise Against Hunger India has served more than 46 million meals and reached over 4 million people through its food security, nutrition and livelihood programmes, working alongside grassroots organizations, rural communities and humanitarian partners across India.


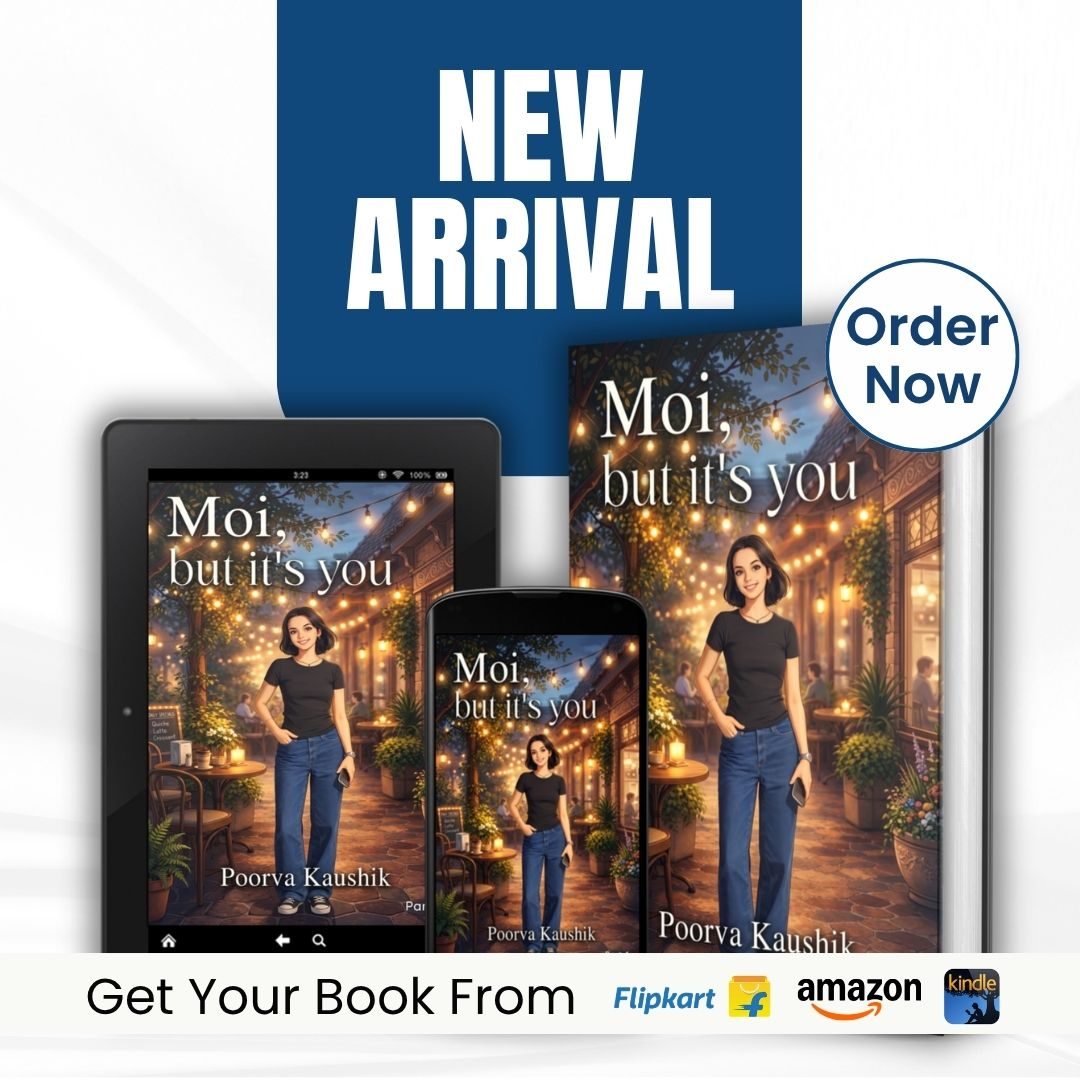
Poorva’s Moi turns school, friendship, family and examinations into an intimate portrait of adolescence—and finds meaning in the ordinary.
There is something disarmingly familiar about Moi, but it’s you, Poorva Kaushik’s debut novel. First published in August 2026, the book follows Mishika, a school-going teenager negotiating friendship, family, academic pressure, self-doubt and the bewildering process of growing up. Rather than constructing adolescence around extraordinary events, Poorva finds her story in the small, recognisable moments that often leave the deepest impressions.
Mishika is an engaging protagonist precisely because she is imperfect. She procrastinates, overthinks, dislikes certain subjects, worries about examinations and frequently finds herself irritated by her twin sister Siya. Their relationship is one of the novel’s most appealing elements: they quarrel, tease and annoy each other, yet their affection remains unmistakable. The book captures the peculiar intimacy of siblings who may fight among themselves but instinctively close ranks when an outsider interferes.
Friendship, however, forms the emotional spine of Moi. Mishika’s experience with Aditi—her childhood friend whose absence leaves behind a complicated mixture of hurt, anger and nostalgia—allows the novel to explore how difficult it can be to forgive without forgetting. Elsewhere, new friendships provide Mishika with companionship during school projects, examinations and everyday crises. A particularly charming early episode sees her agree to a “temporary” best friendship for a week, capturing both the innocence and seriousness with which children approach relationships.
The novel is equally interested in the pressures of teenage life. Exams loom repeatedly over Mishika’s world, but Poorva avoids turning academic anxiety into a conventional motivational lesson. Instead, she shows the messy reality of preparation: distracted studying, exhaustion, panic, humour and the reassuring presence of friends and family. Gradually, Mishika learns that courage does not mean eliminating fear; it means continuing despite it.
A family holiday to Bali provides another important turning point. Away from familiar routines, Mishika begins to reconsider the anxieties that have consumed her. On returning home, she recognises that the journey has changed something within her: the world is still imperfect, but it feels easier to breathe in it.
Poorva’s prose is conversational, youthful and often humorous. Its informal voice, references to contemporary teenage life and frequent self-deprecating observations make Mishika feel less like a constructed literary character and more like someone speaking directly to the reader.
Moi ultimately succeeds because it understands that growing up rarely happens through one dramatic revelation. It happens gradually—in friendships that change, examinations that frighten us, family conversations, mistakes, laughter and quiet moments of self-recognition.
For young readers, Moi offers recognition; for older readers, it offers remembrance. Its greatest achievement is reminding us that the seemingly ordinary days of adolescence are often the ones that become our most enduring stories.
SOC 2 is an independent assurance examination of how a service organization manages customer data against five AICPA Trust Services Criteria. The output is a detailed report, not a formal certificate, that demonstrates the strength of an organization’s information security controls. Many clients now require this report before signing contracts, making it a core component of vendor risk management.
The average data breach now costs more than most organizations can absorb without lasting consequences. According to the 2025 IBM Cost of a Data Breach Report, conducted by the Ponemon Institute and based on data from March 2024 through February 2025, the global average cost fell to $4.44 million, while the United States average reached a record $10.22 million. Those figures explain a shift that procurement and compliance teams across the industry are already responding to. Enterprise buyers are asking vendors to demonstrate their security posture before contracts are signed. For many technology and service providers, the documentation clients request is a SOC 2 report.
This guide explains what SOC 2 means, what the examination covers, and how the audit process works. You will also find guidance on who needs it, the mistakes that most commonly delay organizations, and how independent assurance converts a security claim into verifiable evidence.
What SOC 2 Actually Means
SOC 2 is an independent assurance examination, not a license, a product approval, or a pass or fail badge. It was developed by the American Institute of Certified Public Accountants, which is why you will often see it described as an AICPA SOC 2 examination. The resulting report describes the controls a service organization uses to protect customer data and provides an independent auditor’s opinion on how well those controls are designed and, in some cases, how consistently they operate.
The term “SOC 2 certification” is widely used in commercial and procurement conversations, but it would be more precise to describe the output as an examination report signed by a licensed CPA firm. This does not make the process informal or lightweight. A SOC 2 examination follows the AICPA’s attestation standards and produces documented evidence that clients, regulators, and cyber insurers treat as meaningful.
Importantly, the examination focuses on the specific systems and processes that handle customer information. That targeted scope is what makes SOC 2 relevant to vendor security reviews and what distinguishes it from broader frameworks that assess organizational maturity at a higher level.
The Five Trust Services Criteria
SOC 2 is structured around five Trust Services Criteria defined by the AICPA. Security is the only required criterion. The remaining four are included based on the specific commitments a service organization makes to its clients and the nature of the services it provides.
- Security: Controls that protect systems and data against unauthorized access, including logical access controls, firewalls, intrusion detection, and monitoring.
- Availability: Controls that support system availability in line with agreed service commitments, including backup procedures, disaster recovery plans, and performance monitoring.
- Processing Integrity: Controls that confirm system processing is complete, valid, accurate, timely, and authorized, so that data is handled exactly as intended.
- Confidentiality: Controls that protect information designated as confidential throughout its storage, processing, and disposal lifecycle.
- Privacy: Controls governing how personal information is collected, used, retained, disclosed, and disposed of, consistent with an organization’s stated privacy commitments.
You do not need to include all five criteria in a single examination. Most organizations begin with Security and add additional criteria where their services and client obligations make them relevant.
SOC 2 Type 1 vs SOC 2 Type 2
There are two distinct report types, and the difference between them carries real weight in enterprise procurement discussions.
- SOC 2 Type 1 examines the design of controls at a specific point in time. It addresses one question: are the right controls appropriately designed and in place as of the report date?
- SOC 2 Type 2 examines both the design and the operating effectiveness of controls across a defined observation period, most commonly six to twelve months. It addresses a harder question: did those controls function consistently and as intended over time?
Type 1 is often the first step for organizations that have not yet completed an examination, as it establishes a documented baseline. Type 2 carries more weight with enterprise buyers because it demonstrates that controls held up under real operating conditions across an extended period. Neither report type is universally superior. The appropriate choice depends on your current state of readiness, your timeline, and the specific requirements of your clients.
Who Needs SOC 2 Certification
SOC 2 applies to service organizations that store, process, or transmit customer data on behalf of other businesses. This does not necessarily mean only large enterprises. A growing SaaS company handling client records can face the same security due diligence questions as a long established data center operator.
Organizations commonly asked to produce SOC 2 reports include:
- Cloud platforms and SaaS providers subject to enterprise security due diligence
- Data centers and managed IT service providers
- Fintech and payment processing companies
- Healthcare technology platforms that handle protected information
- Analytics, HR, and marketing technology vendors that hold client data
If a prospective client’s security or procurement team requests independent assurance during vendor onboarding, a SOC 2 report is frequently the specific documentation they are requesting.
Why the Regulatory Climate Is Raising the Stakes
Compliance expectations for data security and supply chain accountability are tightening across major markets. In the United States, SEC cybersecurity disclosure rules, effective for annual reports covering fiscal years ending on or after 15 December 2023, require public companies to report material cybersecurity incidents and describe their risk management processes and governance in their annual filings. This extends scrutiny to the vendors and service providers those companies rely on.
In the United Kingdom, the government published its Cyber Security and Resilience policy statement on 1 April 2025, setting out plans for new legislation that would expand the scope of existing regulations to cover managed IT service providers and certain critical suppliers. The statement also proposes embedding supply chain security requirements directly into the regulatory framework.
The direction across these markets is consistent. Regulators are placing greater responsibility on organizations to demonstrate that their suppliers and service providers meet defined security standards. A SOC 2 report provides documented, independently verified evidence that supports that obligation.
How the SOC 2 Audit Process Works
The examination follows a defined sequence. Understanding the steps helps you plan your timeline and allocate resources appropriately.
- Define scope. Identify which Trust Services Criteria and which systems and services the report will cover.
- Conduct a readiness assessment. Compare your current controls against SOC 2 requirements to identify gaps before the formal examination begins.
- Remediate identified gaps. Strengthen controls, document policies and procedures, and put missing processes in place.
- Select the report type. Decide between Type 1 and Type 2 based on your readiness and the requirements of the clients you are targeting.
- Complete the examination. A licensed, independent CPA firm tests your controls and collects supporting evidence.
- Receive the report. The completed report is issued and can be shared with clients under a confidentiality agreement.
For a Type 2 report, the observation period begins after controls are in place. Organizations that start the process earlier have more time to build a clean evidence record before the formal examination window closes.
Common Mistakes That Delay Organizations
Most delays in completing a SOC 2 examination trace back to a small number of recurring errors.
- Treating the examination as a documentation exercise. Controls must function in practice. Written policies that are not followed in day to day operations will not satisfy an auditor testing operational effectiveness.
- Scoping too broadly at the outset. A focused first report covering core systems is more manageable and more achievable than one that attempts to include every service from the start.
- Failing to collect evidence consistently. Type 2 examinations depend on records that demonstrate controls operated throughout the entire observation period, not just at the beginning or end.
- Skipping the readiness assessment. Organizations that proceed directly to audit without a prior gap review frequently encounter findings that extend timelines and increase costs.
The Business Risk of Waiting
Delay carries a measurable commercial cost. Procurement decisions stall when a buyer’s security team places a hold on a contract pending receipt of a SOC 2 report. Extended sales cycles have direct revenue consequences, particularly where enterprise deals are involved. Given the breach costs documented in the 2025 IBM report and the regulatory developments in the US and UK, organizations that delay independent security assurance face growing commercial and compliance exposure simultaneously.
How Independent Assurance Builds Client Trust
A self assessment of internal controls carries limited credibility in a vendor review. An independent report carries considerably more, because a qualified external auditor, not the organization’s own team, conducted the testing and formed the opinion. That independence is what gives SOC 2 its value in vendor risk management. It reduces the time clients spend on security questionnaires, provides documented answers to due diligence inquiries, and demonstrates that security controls are subject to external scrutiny rather than internal self reporting alone.
How IRQS Supports Your SOC 2 Readiness
IRQS provides certification, assurance, and cybersecurity services to organizations across a range of sectors. For organizations working toward SOC 2 readiness, IRQS offers gap assessment support, control readiness reviews, and guidance on the broader information security work that underpins a credible examination outcome.
Many organizations pursuing SOC 2 are also managing ISO management system requirements or other compliance obligations. Aligning that existing work with SOC 2 preparation, where the controls and documentation overlap, can reduce duplication and make the overall compliance effort more efficient.
IRQS does not make unsupported claims about speed or outcome. What it provides is structured, professional support from a team with direct experience in certification and assurance processes, so that you understand your current position clearly and can take a planned, evidence based approach to the examination.
Take the Next Step
SOC 2 certification has become a standard expectation for many service providers, not an optional differentiator. Understanding the Trust Services Criteria, selecting the right report type, and building a consistent evidence record from early in the process are the factors that determine how smoothly an examination runs. Each of those decisions is easier to make when you have a clear picture of where your controls stand today.
To discuss your SOC 2 requirements and understand what a readiness assessment would involve for your organization, contact IRQS to speak with a specialist about certification and assurance services.
A water testing lab in India analyses drinking, packaged, groundwater, process, borewell and waste water against physicochemical and microbiological parameters. Testing checks whether water is safe for its intended use and supports compliance with standards such as IS 10500 and FSSAI requirements. Food businesses using water as an ingredient are expected to test it periodically at an FSSAI notified or NABL accredited laboratory.
When Clean-Looking Water Fails a Test
Water can look perfectly clear and still carry contamination you cannot see. A borewell that has supplied a facility for years can shift in quality after a change in the water table. A packaged water batch can pass on appearance yet fail on a single microbiological parameter. By the time the problem surfaces in a product complaint or an audit finding, the cost is no longer a laboratory fee. It is stock on hold, a delayed dispatch, or a regulatory query.
This article explains what water testing covers, which parameters matter for different water categories, the Indian standards that apply, and how often you should test. It also covers how to select a NABL accredited water testing laboratory and confirm the right scope for your purpose.
Key takeaways:
- Visual clarity tells you nothing about chemical or microbiological safety.
- Different water categories require different testing parameters.
- IS 10500 and FSSAI requirements govern much of water testing in India.
- Accreditation and approval apply to specific tests, not to a laboratory as a whole.
What Water Testing Is and Why It Matters
Water testing is the laboratory analysis of a water sample against defined parameters. The laboratory measures physical, chemical and microbiological attributes and reports whether they fall within the limits set for the water’s intended use.
The purpose is to replace assumption with evidence. A facility may believe its supply is safe. A test confirms whether it actually is. Water quality analysis in India supports three connected needs at once. It protects health where water is consumed or used in food. It protects processes where water quality affects a product. And it supports compliance where a standard or regulator sets requirements.
This does not mean every sample needs the same panel. A drinking water sample and an industrial effluent sample carry different concerns and different parameters. The appropriate scope follows the water category, its intended use, and the applicable standard.
Why Different Water Categories Need Different Testing
Water is not a single product. The reason for testing, and the parameters that matter, change with the category.
Drinking Water
Drinking water carries a direct health risk. Contaminated supply is a recognised route for waterborne illness, and pathogens such as E. coli and coliform bacteria are common indicators of faecal contamination. Drinking water testing in India typically combines physicochemical checks with microbiological analysis to confirm the water is safe for consumption.
Packaged Water
Packaged water is a regulated product, not just a supply. Packaged water testing applies to packaged drinking water and packaged natural mineral water, where both product quality and applicable standards matter. A batch that looks acceptable can still fail on a microbiological or chemical parameter, which is why testing supports release rather than assumption.
Groundwater and Borewell Water
Groundwater quality can change over time. A groundwater testing lab assesses supply drawn from below the surface, where contamination can enter through the surrounding soil, nearby activity or a shifting water table. Borewell water testing is relevant for facilities and premises relying on a borewell, because a source that tested clean once may not stay that way.
Process Water and Industrial Water
Process water can affect the product it touches. Process water testing matters where water becomes part of a manufacturing operation, a cleaning step, or the finished product itself. Industrial water testing also supports equipment reliability, since parameters such as hardness and dissolved solids can affect plant and machinery.
Wastewater
Wastewater carries environmental obligations. Wastewater testing in India assesses domestic sewage and industrial effluent against discharge related requirements, and it often connects to environmental compliance work overseen by pollution control authorities.
Swimming Pool Water
Swimming pool water needs regular monitoring. Parameters such as residual chlorine, pH and microbiological quality determine whether pool water is safe for use, and these can drift quickly with load and temperature.
Key Water Testing Parameters
Water testing parameters fall into three groups. The right combination depends on the water category and its intended use.
Physical Parameters
Physical parameters describe attributes you can often detect through the senses, measured objectively in the laboratory. These include colour, turbidity, odour and taste. They give an early indication of water quality, though they do not, on their own, confirm safety.
Chemical Parameters
Chemical parameters measure dissolved substances that affect quality and safety. Physicochemical water analysis commonly covers pH, hardness, total dissolved solids, chlorides, and residual chlorine, along with metals and other constituents depending on the source. Some parameters, such as pH, turbidity and residual chlorine, are sensitive to storage and are best checked promptly after sampling.
Microbiological Parameters
Microbiological parameters detect harmful organisms. Microbiological water testing checks for indicators of contamination such as coliforms and E. coli, which signal a food safety or public health concern. For drinking and packaged water, this analysis is central rather than optional.
The key distinction is this. Physical and chemical results describe the character of the water, while microbiological results address contamination risk. Most drinking and packaged water assessments need all three groups together.
Indian Standards and Regulatory Context
Water testing in India is guided by recognised standards. Knowing which one applies helps you define the correct scope.
IS 10500 is the Bureau of Indian Standards specification for drinking water. IS 10500 water quality standards set acceptable limits and permissible values for physical, chemical and microbiological parameters in drinking water. It is the common reference point for assessing whether water is fit for human consumption.
For food businesses, FSSAI requirements add a further layer. FSSAI guidance provides that food businesses using water as an ingredient in food should get the water tested against BIS IS 10500, other than radioactive parameters, at defined intervals, and FSSAI material indicates such testing at least once every six months from an FSSAI notified or NABL accredited laboratory. Requirements can change, so confirm the current provision that applies to your operation before finalising a testing schedule.
Broader water quality standards are also referenced by bodies such as APHA, CPCB and WHO, with the applicable norm depending on the water’s purpose. Packaged drinking water and packaged natural mineral water carry their own BIS specifications relevant to those products.
Importantly, a test report is analytical data. It supports compliance decisions, but a report on its own does not constitute regulatory approval. Compliance depends on the applicable standard, the water’s intended use, and how the data is applied.
When and How Often to Test Water
Testing once gives you a snapshot, not a trend. Frequency should follow the water category, its use, and the applicable requirement rather than a single fixed habit.
Consider testing in these situations:
- On a defined schedule for drinking water, and at least once every six months where you use water as a food ingredient, subject to the current FSSAI provision.
- Before releasing a batch of packaged water, in line with the applicable product standard.
- Periodically for groundwater and borewell supply, since source quality can shift over time.
- After any change to the source, treatment system or storage arrangement.
- Following a contamination concern, an unusual taste or odour, or an unexplained quality failure.
- Routinely for wastewater, in line with discharge related obligations.
Routine testing also builds a record. When results begin to move, a facility can often identify a developing problem before it affects health, product or compliance.
How to Select a NABL Accredited and FSSAI Approved Water Testing Lab
Choosing a laboratory is a technical decision as much as a commercial one. A few markers help you compare providers on more than price.
- Accreditation scope. NABL accreditation confirms technical competence for specific named tests. Check that your water category and parameters fall within the accredited scope of the NABL accredited water testing laboratory you are considering.
- Relevant approval. For food related testing, confirm FSSAI approved water testing status appropriate to your purpose, since FSSAI expects testing from an FSSAI notified or NABL accredited laboratory.
- Parameter coverage. Confirm the laboratory can handle the physical, chemical and microbiological parameters your category requires.
- Method suitability. The laboratory should apply validated methods appropriate to your parameters and reporting limits.
- Sampling capability. Correct sampling and prompt handling affect the reliability of results, particularly for parameters such as pH, turbidity and residual chlorine.
- Turnaround. Confirm a realistic timeline, noting that microbiological analysis requires incubation time.
Accreditation and approval both apply to defined tests and purposes. It would therefore be inaccurate to assume that a laboratory holding NABL accreditation is accredited for every water test it offers. Always check the specific parameter, on your specific water category, against the accredited scope.
How ISSPL Testing Lab Supports Water Testing
ISSPL Testing Lab is operated by IRCLASS Systems and Solutions Pvt Ltd, an independent analytical testing service provider in India. Water testing sits within its dedicated water testing services.
The coverage spans the main water categories. ISSPL provides testing for drinking water, groundwater, borewell water, packaged drinking water, packaged natural mineral water, processed water and wastewater, among other applications. This range matters because a food manufacturer, a packaged water brand and an industrial facility rarely need the same panel, and a single laboratory that covers several categories reduces the number of providers you coordinate.
On accreditation and approval, ISSPL states that its laboratory holds recognitions including NABL, accredited against ISO/IEC 17025, and FSSAI, alongside other approvals relevant to its wider testing work. For a food business required to test water as an ingredient, that combination is directly relevant, because FSSAI expects such testing from an FSSAI notified or NABL accredited laboratory. The specific parameters should still be confirmed against the applicable scope, since a recognition does not cover every test by default.
ISSPL operates across India with sampling support, which matters for water testing, where correct sample collection and prompt handling directly affect the reliability of the result. For food businesses, packaged water brands, manufacturers, industries and institutions, this allows water testing to be planned around the actual requirement rather than split across several providers.
This does not mean every business needs the full range of services. The relevant point is that the scope can be matched to your water category, your parameters and your purpose.
Frequently Asked Questions
What parameters are checked in water testing?
Water testing covers physical parameters such as colour, turbidity and odour, chemical parameters such as pH, hardness, total dissolved solids and residual chlorine, and microbiological parameters such as coliforms and E. coli. The exact combination depends on the water category and its intended use.
How often should food businesses test their water?
FSSAI guidance indicates that businesses using water as an ingredient should test it against BIS IS 10500, other than radioactive parameters, at least once every six months from an FSSAI notified or NABL accredited laboratory. Requirements can change, so confirm the current provision that applies to your operation.
What is IS 10500 in water testing?
IS 10500 is the Bureau of Indian Standards specification for drinking water. It sets acceptable and permissible limits for physical, chemical and microbiological parameters, and it serves as the common reference for assessing whether water is fit for human consumption.
Does a water test report guarantee regulatory compliance?
No. A report provides analytical data on the sample tested. Regulatory compliance depends on the applicable standard, the water’s intended use, and how the data is applied. A test report supports compliance decisions but does not by itself constitute approval.
Can one laboratory test drinking, packaged, groundwater and waste water?
Yes, where the laboratory holds coverage across those categories. A single provider reduces coordination and keeps reporting consistent. Confirm that each required test, on your specific water category, falls within the accredited or approved scope.
How much does water testing cost in India?
Cost depends on the water category, the number of parameters, the test methods and any sampling support required. Because these factors vary, pricing is best confirmed against a defined scope rather than a single fixed rate.
How long does water testing take?
Turnaround depends on the parameters requested. Microbiological analysis requires incubation time, so it typically takes longer than physical and chemical checks. Sharing your full parameter list and water category at the enquiry stage allows the laboratory to advise a realistic timeline.
Test Your Water Before It Becomes a Problem
Water quality rarely announces itself. Clear water can carry contamination, and a source that tested well once can change with time, use or season. Testing turns an assumption into verified data, and it does so while there is still time to act, whether the concern is health, product quality or compliance.
Businesses requiring water testing can contact ISSPL Testing Lab to discuss their water category, intended use, applicable parameters and the right testing scope. A short conversation about your source, your purpose and the standard that applies is usually the fastest way to define the correct panel before a quality or compliance issue arises.


Advocate Jatin Sharma Calls for ‘Justice Corridors’ to Strengthen Cross-Border Trade at High Level Diplomatic Meet 2026

Book Review | Moi, but it’s you by Poorva Kaushik

SOC 2 Certification Explained: What It Is and Why Clients Now Expect It

Redfox Overseas: Customize Your Own Energy Drink and Stand Out in the Market

Zamzam Company CEO Chhote Bhai-Bade Bhai gave a grand welcome to Indian writer Devhari Sirvi in Dubai

Shikha Sharma: The Fashion Journalist, Blogger, and Plus-Size Model Taking the Industry by Storm
-
 Brandpost2 years ago
Redfox Overseas: Customize Your Own Energy Drink and Stand Out in the Market
-
 Brandpost2 years ago
Zamzam Company CEO Chhote Bhai-Bade Bhai gave a grand welcome to Indian writer Devhari Sirvi in Dubai
-
 Fashion2 years ago
Shikha Sharma: The Fashion Journalist, Blogger, and Plus-Size Model Taking the Industry by Storm
-
Entertainment1 year ago
Lucky Roxx’s “Yadav Ki Pukar” Goes Viral! Youth Celebrate Unity & Power
-

 Entertainment9 years ago
New Season 8 Walking Dead trailer flashes forward in time
-
Entertainment9 years ago
Meet Superman’s grandfather in new trailer for Krypton
-
Uncategorized2 years ago
Hello world!
-
 Brandpost2 years ago
From Local Hero to National Icon: Satyam Yadav’s Journey with TwentyOne