
Technology
Security Can’t Be an Afterthought: How App Dev Company Builds It Into Every Project Stage

Modern mobile applications routinely handle customer accounts, payment details, and sensitive personal data, making security a foundational requirement rather than a feature to bolt on before launch. App Dev Company, working with its team of mobile app developers, frames security as something considered throughout the entire development process rather than addressed only at the end.
According to the company, this means implementing industry best practices including secure authentication, encrypted communication, API protection, and regular security testing across a project’s full development lifecycle, rather than treating a pre-launch security review as sufficient on its own. Retrofitting security into an application that was designed without it in mind from the start is generally more difficult and expensive than building security considerations into the architecture from day one.
Why Security Failures Damage More Than Data
A security breach affects more than the immediate technical or financial cost of remediation — it damages customer trust in ways that can persist well beyond the incident itself, particularly for applications handling financial transactions or sensitive personal information where users have limited tolerance for perceived carelessness with their data. Professional mobile app developers generally treat security and trust-building as closely linked concerns, since users increasingly factor a company’s data-handling reputation into their willingness to use an application at all.
What Ongoing Security Actually Involves
Security isn’t a one-time implementation but an ongoing practice, since new vulnerabilities are discovered continuously across software ecosystems, meaning applications require regular security testing and updates well after initial launch to remain protected against threats that didn’t exist when the app was first built. An App Dev Company committed to this ongoing model generally treats security patching as part of standard post-launch maintenance rather than a separate, occasionally addressed concern.
Authentication and API Protection as Baseline Requirements
Secure authentication and API protection represent baseline security requirements for any application handling user accounts, since weak authentication or an unprotected API can expose an entire application’s data regardless of how well other parts of the system are secured. Encrypted communication between an app and its backend servers similarly protects data in transit, closing a common vulnerability point that attackers frequently target when other defenses are otherwise reasonably strong.
For businesses evaluating any development partner’s security practices, asking specifically how authentication, encryption, and ongoing security testing are handled throughout a project — rather than assuming security is uniformly addressed by default — remains a reasonable step given how consequential a security failure can be for both a business and its customers.
Regulatory requirements around data protection have also grown more demanding in many markets in recent years, meaning applications handling personal or financial data increasingly need to satisfy specific compliance frameworks in addition to general security best practices, a consideration that adds complexity beyond technical security measures alone.
Third-party security audits, conducted by an independent party rather than the development team itself, offer an additional layer of assurance for applications handling especially sensitive data, since an internal team reviewing its own work may miss vulnerabilities that a fresh, independent set of eyes would more readily identify.
Visit- https://appdev.company/
Technology
New UPI app Pay10 available on Google Play Store
Pay10 launched its Customer App on the Google Play Store on September 23, offering NPCI-powered UPI payments, a prepaid wallet, instant bank transfers and zero-fee wallet-to-wallet transfers within its own ecosystem.
A new UPI-based payments app, Pay10, is now available on the Google Play Store.
It launched on September 23, 2026.
The app offers UPI payments, a prepaid wallet and instant bank transfers.
An Apple App Store version is expected to follow.
It is powered by NPCI infrastructure.
Users can make payments through QR codes or UPI IDs.
The app also allows users to add funds to a prepaid wallet through UPI.
It enables real-time bank transfers to a user’s own or other bank accounts.
Within the Pay10 ecosystem, users can make instant, zero-fee wallet-to-wallet transfers using a mobile number or QR code.
The company says the platform uses bank-grade encryption to support secure payments.
Pay10 has designed the app around a tiered KYC framework, letting users start with limited KYC and upgrade for higher transaction limits.
Customer support is available through 24/7 human assistance, alongside an AI-powered grievance system.
UPI has become the dominant digital payments rail in India, used for both everyday retail transactions and large-scale transfers.
New UPI-based apps continue to enter the Indian market as digital payments adoption grows.
NPCI is the umbrella organisation that operates UPI and other retail payment systems in India.
India’s digital payments ecosystem has expanded rapidly over the past decade, driven largely by UPI adoption.
KYC, or Know Your Customer, verification is a standard regulatory requirement for financial and payments apps in India.
Wallet-based payment apps typically operate alongside UPI rather than replacing it, offering additional features like instant peer transfers.
The Reserve Bank of India regulates digital payment providers and prepaid payment instrument issuers in the country.
Pay10 launched its Customer App on the Google Play Store on September 23, 2026.
The company said an Apple App Store version will follow.
The app is built on infrastructure powered by the National Payments Corporation of India (NPCI).
Smartphone apps (representative image), Wikimedia Commons, CC BY-SA 4.0
Technology
SEMICON India 2026: How the fifth edition unfolded
The government unveiled the Semicon 2.0 roadmap at SEMICON India 2026, with a Rs 1.27 lakh crore outlay across six pillars aimed at creating close to one lakh jobs and supporting at least 200 chip-design start-ups.
SEMICON India 2026, the fifth edition of the event, was inaugurated by PM Modi on September 17.
The three-day conference at Yashobhoomi, New Delhi, brought together more than 600 companies from 52 countries.
It was themed ‘Silicon to Systems: Building the Ecosystem’.
The event saw the unveiling of the Semicon 2.0 roadmap, with an outlay of Rs 1.275 lakh crore.
The roadmap is structured around six pillars, from chip design to talent development.
It targets training 100,000 technicians for cleanroom and factory-floor roles.
Semicon 2.0 aims to support at least 200 chip-design start-ups and companies.
Investment commitments of about Rs 1 lakh crore, or $11-12 billion, have been received under the programme so far.
SEMICON India 2026 was the fifth edition of the event, inaugurated by Prime Minister Narendra Modi on September 17.
The three-day conference brought together more than 600 companies from 52 countries.
SEMICON India 2026 was themed ‘Silicon to Systems: Building the Ecosystem’.
The event was organised by the India Semiconductor Mission, the Ministry of Electronics and Information Technology, and SEMI.
Semicon 2.0 is described as the next phase of India’s broader semiconductor programme.
India has set a longer-term target of building a $200 billion domestic semiconductor market.
The India Semiconductor Mission was set up to coordinate the country’s chip manufacturing and design push across ministries.
Global semiconductor supply chains have been a focus for many governments in recent years, given their importance to electronics, automotive and defence industries.
India’s earlier semiconductor programme, under the original Semicon India initiative, approved several fabrication and packaging projects before Semicon 2.0 was unveiled.
State governments have also announced incentives to attract semiconductor investment alongside the central government’s programme.
Chip design, fabrication and packaging each require different kinds of infrastructure, talent and capital investment.
The government unveiled the Semicon 2.0 roadmap at SEMICON India 2026, held at Yashobhoomi in New Delhi.
Semiconductor wafer (representative image), Wikimedia Commons, CC BY-SA 4.0
Technology
Starship to fly reused heatshield tiles for the first time
SpaceX has pushed back Starship Flight 14, the rocket’s first attempt at a full orbital mission, from September 22 to September 28, 2026, after moving Super Heavy Booster 21 to the launch pad at Starbase, Texas.
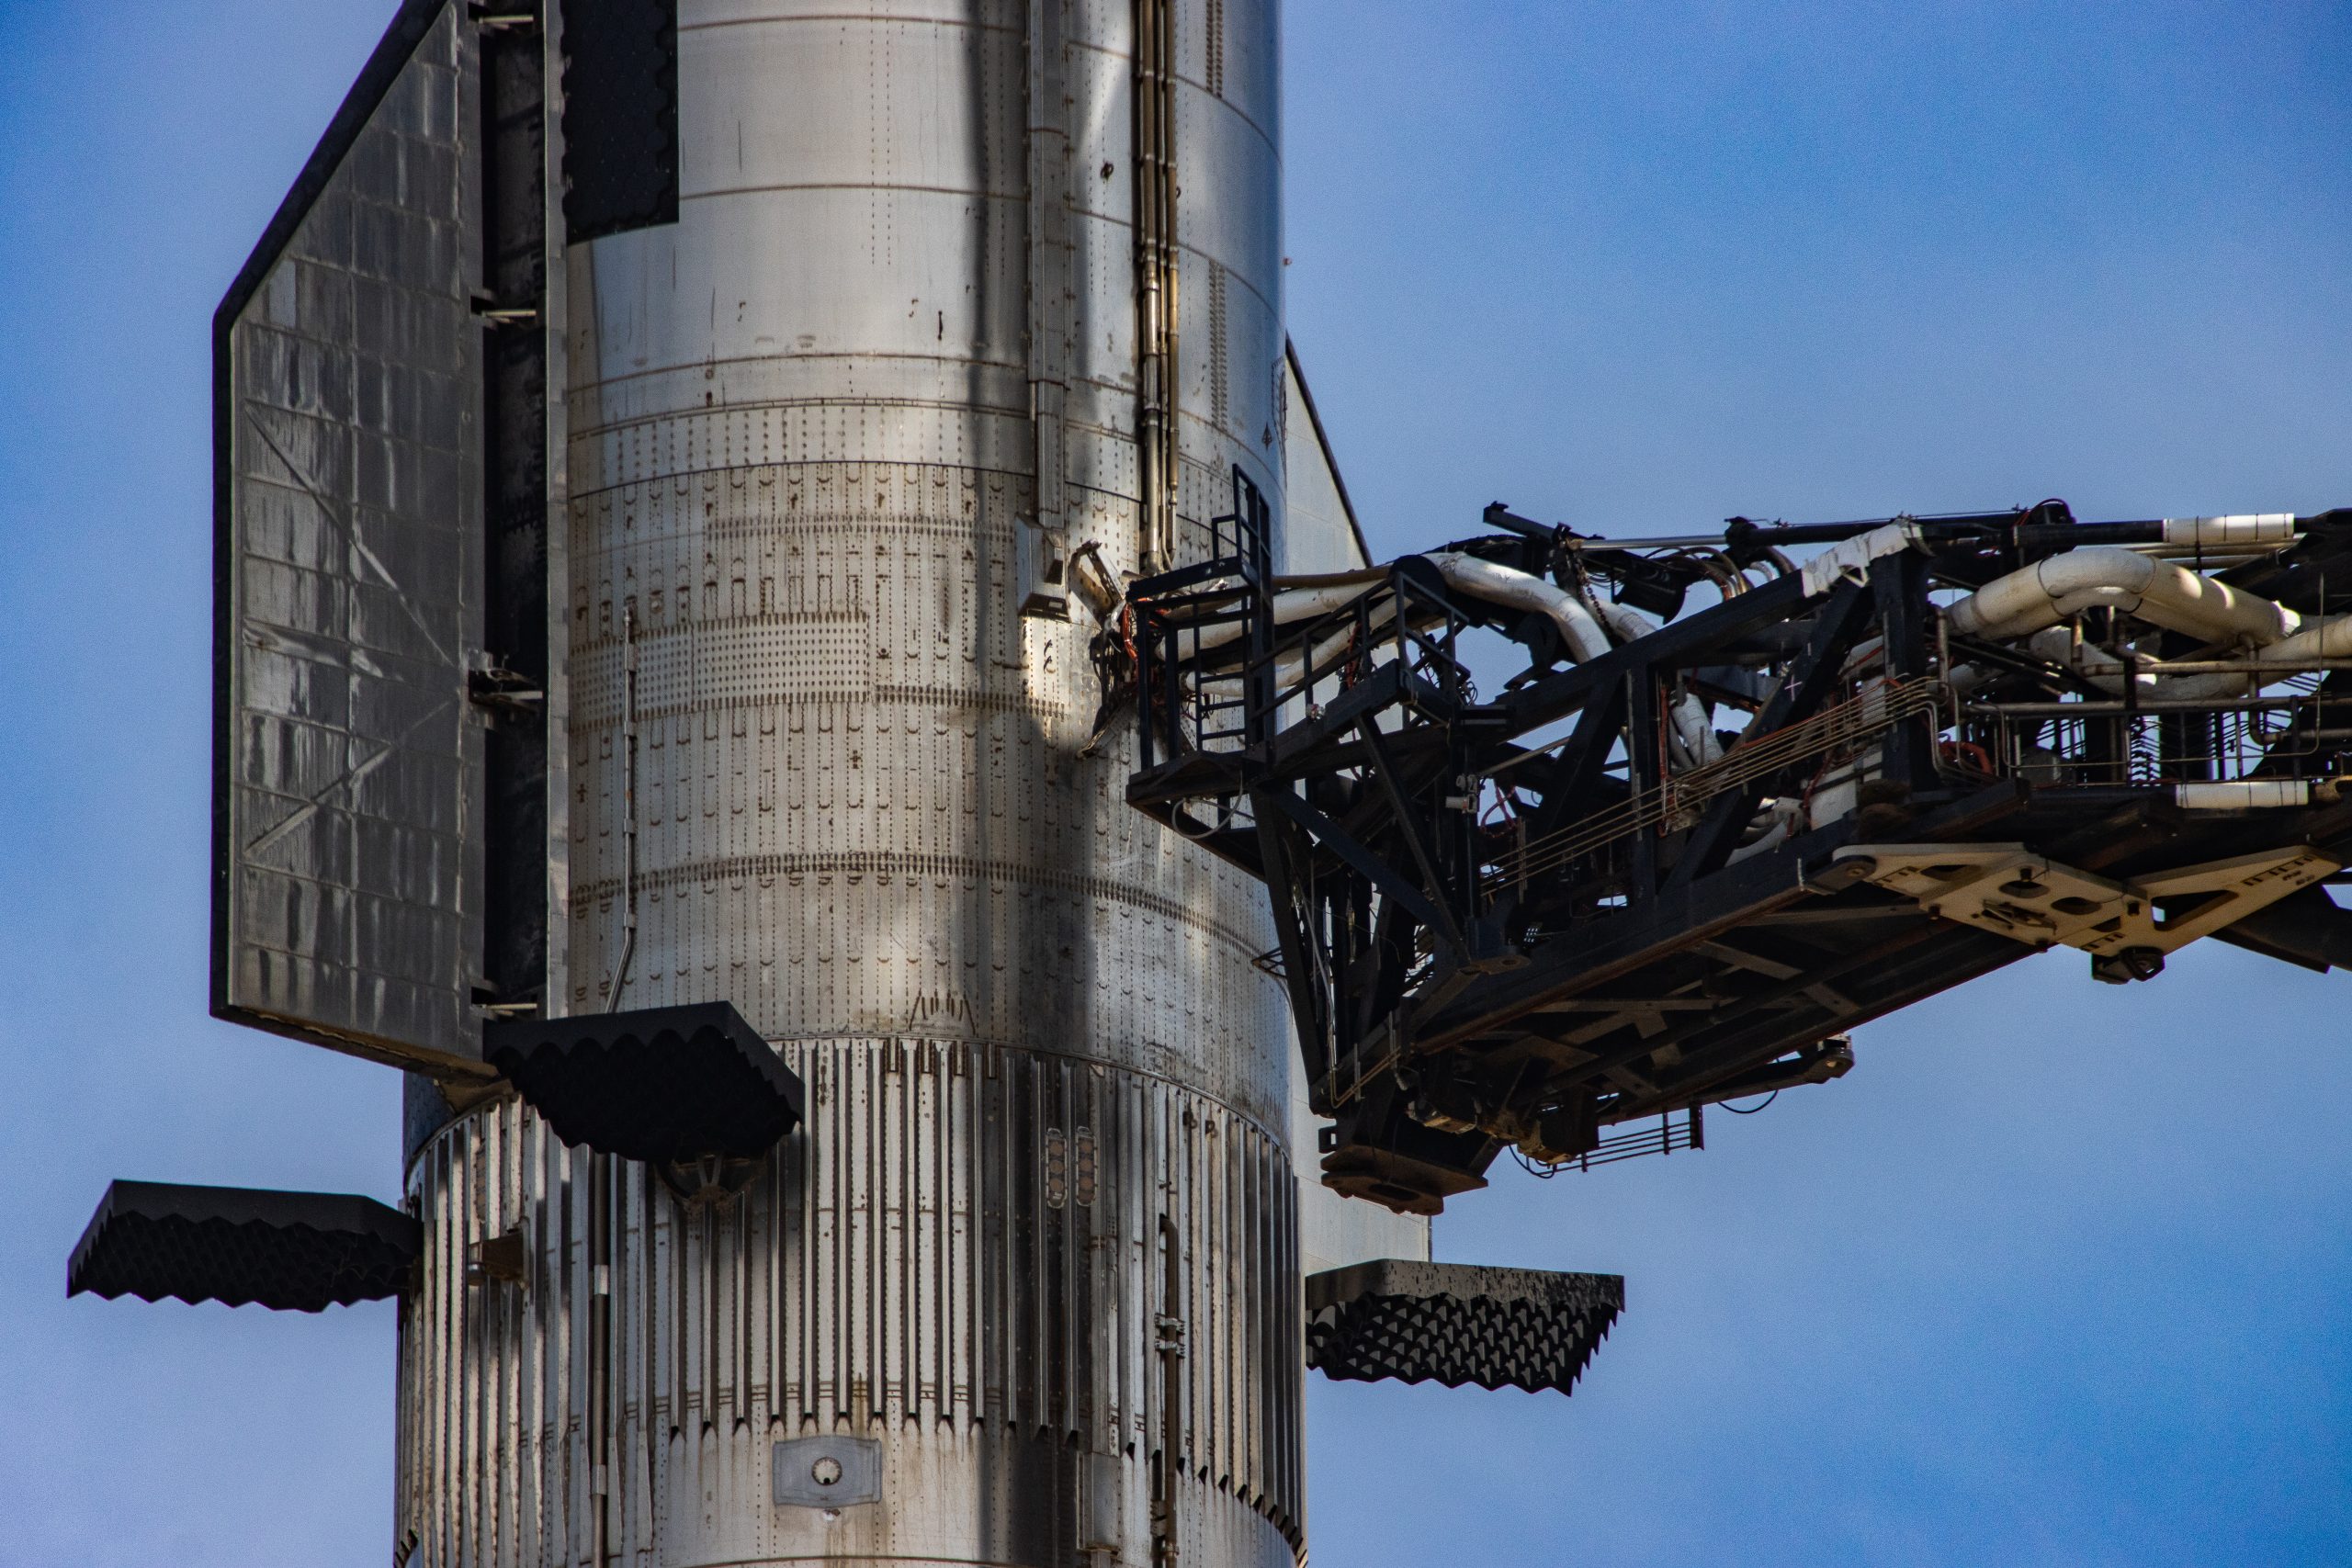
SpaceX plans to fly two previously recovered heatshield tiles on the upcoming Starship Flight 14, a first for the programme.
It marks an initial step toward reusing Starship’s heatshield tiles across missions.
The flight is now targeted for September 28, 2026, after a delay from September 22.
Flight 14 will use Super Heavy Booster 21 and Ship 41.
The mission aims to be Starship’s first full orbital flight.
Booster 21 completed a 33-engine static fire test, and Ship 41 completed a 6-engine static fire test ahead of launch.
Flight 14 is intended to be Starship’s first true orbital mission; earlier flights had only flown ‘passively safe’ suborbital trajectories that avoided a full orbit.
The mission plan calls for deploying 26 Starlink V3 satellites during the flight.
Ship 41 is expected to complete six orbits of Earth before a planned splashdown in the Pacific Ocean, about 10 hours after liftoff.
Unlike some earlier flights, Super Heavy Booster 21 will not attempt a catch at the launch tower; instead it is set to perform a controlled splashdown in the Gulf of Mexico.
SpaceX said it made unspecified ‘modifications to hardware and software’ to address issues seen on the previous Starship flight.
For the first time on a Starship mission, SpaceX plans to fly two previously recovered heatshield tiles, marking an initial step toward heatshield tile reuse.
Starship launches from Starbase, SpaceX’s private launch site near Boca Chica in South Texas.
Starship is designed to be fully reusable and is central to SpaceX’s plans for satellite deployment, Moon missions under NASA’s Artemis programme, and eventual Mars missions.
The vehicle consists of the Super Heavy booster as the first stage and the Starship upper stage, both powered by SpaceX’s Raptor engines.
SpaceX delayed Starship Flight 14 from September 22 to September 28, 2026, without publicly specifying a reason.
SpaceX Starship full stack, Starbase, Texas (representative image), Wikimedia Commons, CC BY-SA 4.0


Mangrove Ecosystems: Nature’s Living Shield Against Climate Change and Coastal Disasters

Mumbai airport slot cuts: What happens next for passengers

Vivil Raj S: A Technology Entrepreneur Connecting IT, Marketing and Digital Business Solutions

Redfox Overseas: Customize Your Own Energy Drink and Stand Out in the Market

Zamzam Company CEO Chhote Bhai-Bade Bhai gave a grand welcome to Indian writer Devhari Sirvi in Dubai

Shikha Sharma: The Fashion Journalist, Blogger, and Plus-Size Model Taking the Industry by Storm
-
 Brandpost2 years ago
Redfox Overseas: Customize Your Own Energy Drink and Stand Out in the Market
-
 Brandpost2 years ago
Zamzam Company CEO Chhote Bhai-Bade Bhai gave a grand welcome to Indian writer Devhari Sirvi in Dubai
-
 Fashion2 years ago
Shikha Sharma: The Fashion Journalist, Blogger, and Plus-Size Model Taking the Industry by Storm
-
Entertainment2 years ago
Lucky Roxx’s “Yadav Ki Pukar” Goes Viral! Youth Celebrate Unity & Power
-

 Entertainment9 years ago
New Season 8 Walking Dead trailer flashes forward in time
-
Entertainment9 years ago
Meet Superman’s grandfather in new trailer for Krypton
-
Uncategorized2 years ago
Hello world!
-
 Brandpost2 years ago
From Local Hero to National Icon: Satyam Yadav’s Journey with TwentyOne